ON-DEMAND WEBINAR

Insurance and Cybersecurity Considerations for Psychologists: Am I Meeting My Cyber Insurance Requirements?

Originally recorded on October 30, 2026
  • 3 Hours
  • 1 Evaluation
  • $115.00
  • Beginner to Advanced
Empty space, drag to resize
overview
Multifactor authentication, device encryption, regular backups, patching and annual staff training are only part of the equation. You have to sign off on these measures and be ready to prove they are in place. In this three-hour session, Kelly Paisley, who runs an IT company that specializes in answering these questions, sits down with Chris Pawluk to discuss what psychologists are actually being asked to attest to, where the gaps typically occur, and what a defensible file looks like before an insurer, broker or regulator asks for one.
Empty space, drag to resize
Certification included
This webinar is eligible for 3 Continuing Education (CE) Credits on behalf of the Canadian Psychological Association.
ABOUT THE WEBINAR
LEARNING OBJECTIVES
PRESENTATION MATERIALS
DISCLOSURE
Empty space, drag to resize
In the course player, you will have access to the following items:
Once you pass the evaluation, you can fill out your Certificate of Completion for immediate download.
Empty space, drag to resize
The session begins by exploring why cyber insurance changes the conversation. For years, cybersecurity in private practice was a matter of professional judgment and privacy policies. It is now a set of contractual conditions requiring a signature, with the added challenge that regulators, insurers, and actual working systems each have slightly different expectations.

From there, the session examines one of the most common beliefs: all patient data is stored in the EMR, and because the EMR is secure and backed up, the practice is protected. While that claim is often true, it is rarely complete. Client information also exists in emails, downloaded reports, scoring platforms, laptops and phones, cloud storage that has not been audited, and increasingly, AI tools. The session follows these information trails and connects them to data-retention and system-security decisions.

The middle portion of the session focuses on practical examples. Participants explore a green, yellow, and red framework for prioritizing cybersecurity risks, followed by several insurance-readiness scenarios, including a misdirected report, a compromised email account, a departing staff member whose access has not been revoked, and an AI scribe that has not been properly vetted. Each scenario focuses on practical solutions rather than theoretical approaches.

The final hour focuses on the documentation itself. Participants learn what a minimum viable insurance-readiness record contains, how to assemble one without an IT department, and what steps to take during the first hour following an incident, including who needs to be notified and in what order.
Empty space, drag to resize
Upon completing this webinar, participants will be able to:

1. Identify the safeguards commonly required on cyber insurance applications, including multifactor authentication, device encryption, backups, patching, endpoint protection, and staff training, and explain what each one means in the context of a psychology practice.
2. Map where client information actually lives across their practice systems, including practice management software, email, cloud storage, devices, scoring platforms, and AI tools, and connect that map to data-retention and system-security decisions rather than assuming everything stays in the EMR.
3. Apply a green, yellow and red framework to triage cybersecurity and privacy risks in their own practice, distinguishing defensible baselines, workflows needing review, and items requiring prompt correction.
4. Assemble a minimum viable insurance-readiness file that documents systems, safeguards, access, vendors, and incident-response contacts in a form defensible to an insurer, broker, or regulator.
5. Describe the first response steps after common incidents, including containment, evidence preservation, and reporting obligations to broker, insurer, and privacy bodies.
Mr. Paisley is President and CEO of The I.T. Company, a managed services and cybersecurity provider, and The I.T. Company provides IT services to Hexagon Psychology. This session is educational and is not a sales presentation. No product, platform, or vendor is endorsed, and Mr. Paisley receives no speaker fee from Hexagon Training for this presentation.
Testimonials

What Our Learners Had To Say

I really enjoy the format, the discussion between the two and answering our questions alongside the presentation.  The examples were very useful.
Excellent Presentation. Very helpful and informative.
I want every therapist I know to take this [course], I also plan on sharing it with my colleagues.
MEET THE SPEAKER

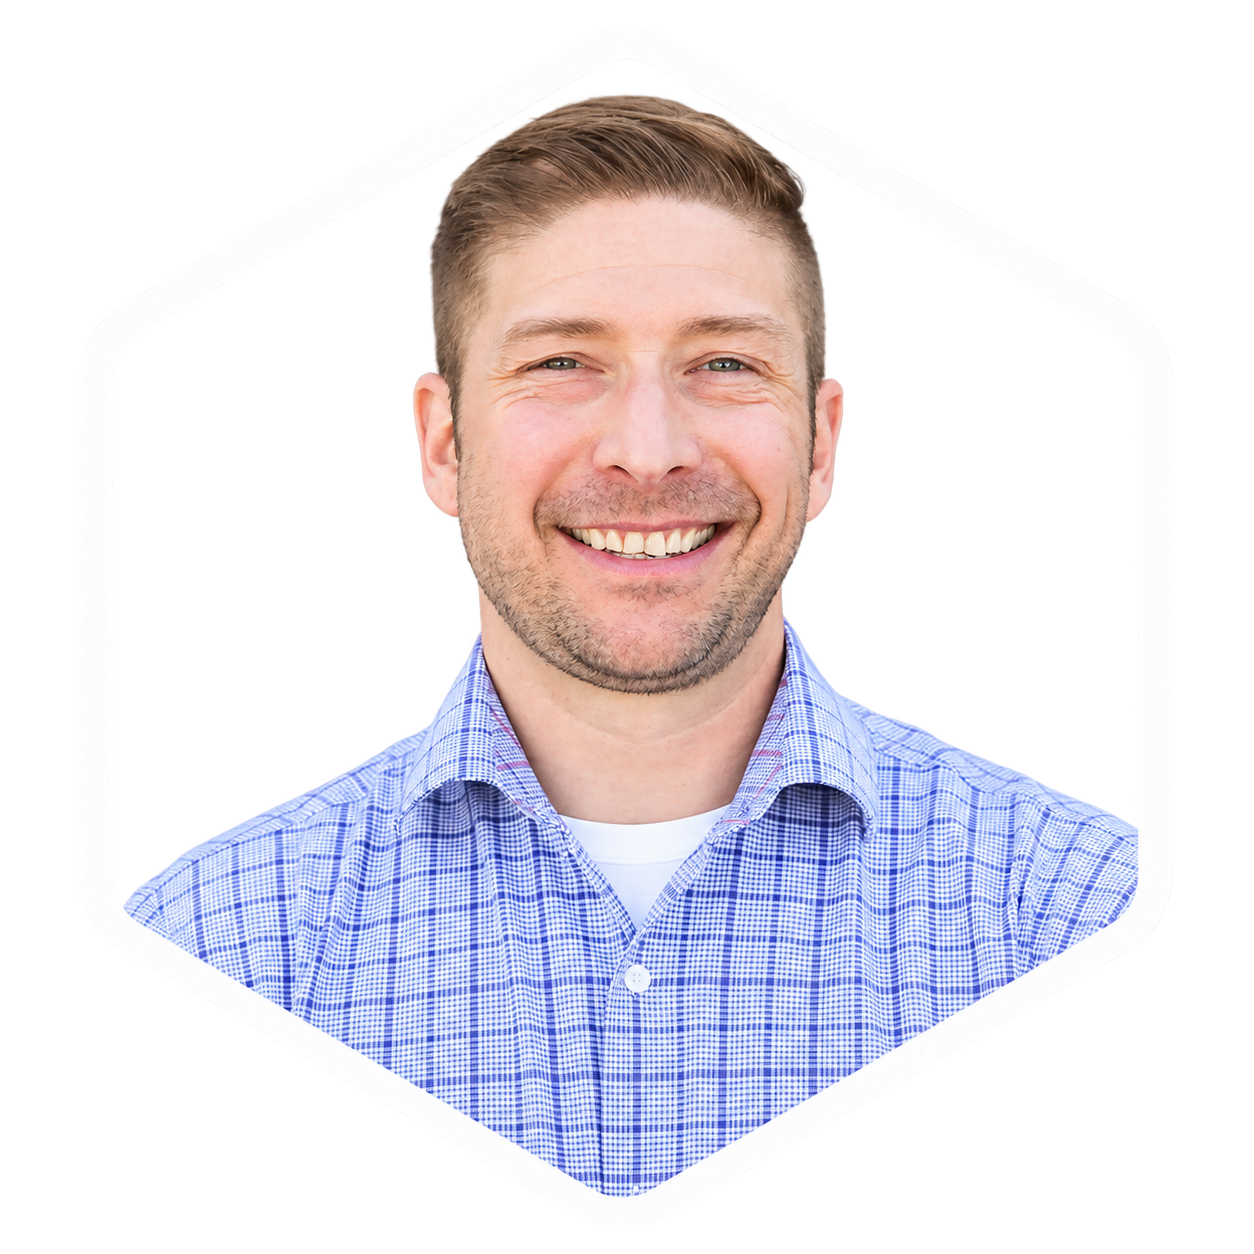
Kelly Paisley, CEO

Kelly Paisley, President and CEO, The I.T. Company

Kelly Paisley is President and CEO of The I.T. Company, a managed services and technology consulting firm established in 2008. His path into IT began early, taking apart the family electronics and teaching himself to put them back together before anyone noticed, and he was working as an IT administrator shortly after college. 

Two decades on, his focus has moved from the helpdesk to strategy: growth planning, business consulting, and helping organizations use technology to increase revenue while reducing their digital vulnerabilities. 

The I.T. Company provides managed IT services, cloud solutions, cybersecurity and IT consulting, and is an approved advisor under the Canada Digital Adoption Program. Kelly works with professional practices on cybersecurity, managed services and
insurance readiness. Outside work he spends most of his time with his son, boxing, reading and at the occasional comic convention.
Turn insights into action. Enroll today and start applying
what you learn immediately.